Docker is an open-source platform for building, shipping and running applications in containers. A container bundles your app with its runtime, libraries and config, and runs it as an isolated process on a Linux kernel. The same image behaves the same way on your laptop, on a CI runner and on a production server.
Docker didn't invent containers. The Linux kernel had the building blocks, namespaces and cgroups, years before Docker was released in 2013. What Docker did was make them easy to use: one image format, one command-line tool and a public registry full of ready-made images.
Every command in this guide was run on Docker Engine 29.4 with Docker Compose v5. The outputs are real, trimmed where marked with ....
Containers vs virtual machines
The classic way to run several applications on one server is virtualization. A hypervisor splits the physical machine into virtual machines (VMs), and each VM boots its own kernel and a full operating system. Isolation is strong, but every VM costs gigabytes of disk and memory and takes a while to boot.
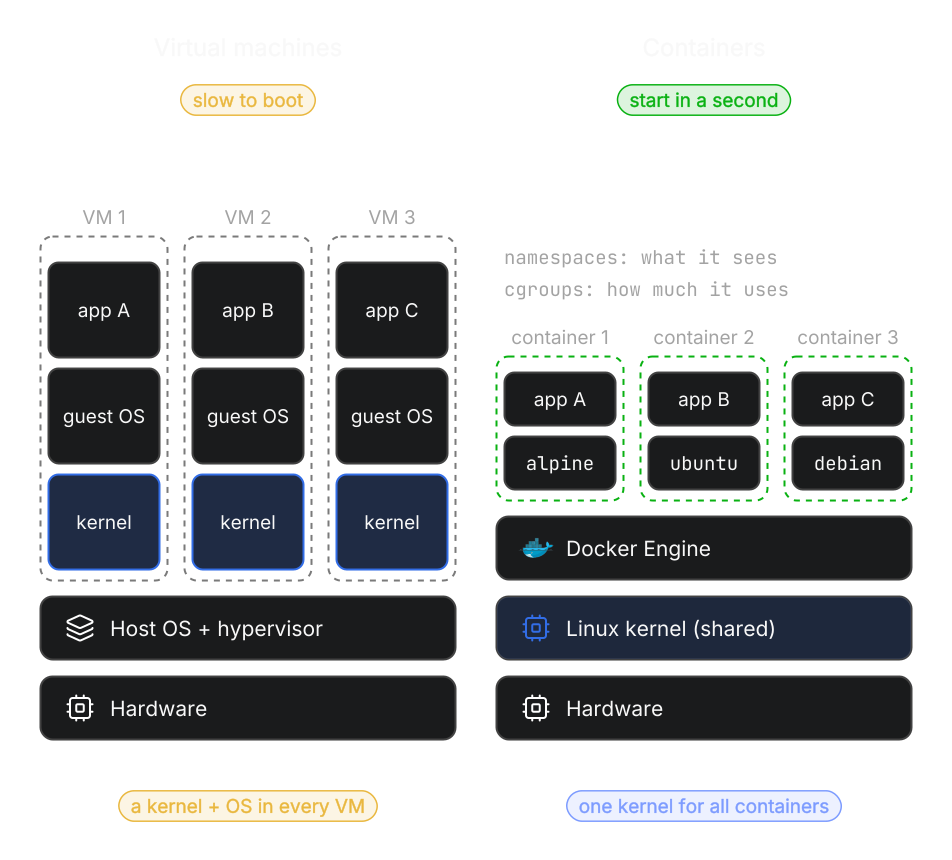
A container skips the hypervisor and the guest kernel. It's a regular process on the host, fenced off by features of the Linux kernel:
- Namespaces control what the process can see: its own process tree, network interfaces, mounts, hostname and users.
- Control groups (cgroups) control how much it can use: CPU, memory, disk I/O and the number of processes.
- Its own root filesystem, unpacked from the image, so the process sees the image's files instead of the host's.
A container is not an empty box without an operating system. An Alpine or Ubuntu image ships the distribution's userland: shell, libc, package manager. What a container doesn't have is its own kernel. All containers on a host share the host's kernel, and you can see it yourself:
shell
1docker run --rm alpine:3.24 uname -r2docker run --rm ubuntu:24.04 uname -r3docker run --rm ubuntu:24.04 head -2 /etc/os-releaseshell
16.12.76-linuxkit26.12.76-linuxkit3PRETTY_NAME="Ubuntu 24.04.5 LTS"4NAME="Ubuntu"Two different distributions, one kernel. Here it's the kernel of the small Linux VM that Docker Desktop runs on a Mac. On a Linux server you'd see the server's own kernel version.
The PID namespace is just as easy to spot. Inside a container, ps sees only its own processes, and the first one gets PID 1:
shell
1docker run --rm alpine:3.24 psshell
1PID USER TIME COMMAND2 1 root 0:00 psWhat this means in practice:
- Containers are light. They start in about a second, an image is often tens of megabytes, and one host runs dozens or hundreds of them.
- Isolation is weaker than in a VM. A shared kernel means a kernel vulnerability affects every container on the host. For untrusted multi-tenant workloads, VMs (or sandboxed runtimes built on them) are still the safer choice.
- Linux containers need a Linux kernel. That's why Docker Desktop on macOS and Windows runs a Linux VM under the hood.
Containers don't replace virtualization, they sit on top of it more often than not. In the cloud your containers usually run on VMs, like EC2 instances or Kubernetes worker nodes. What containers remove is the need for a separate VM per application, and that's where the savings on cost and server utilization come from.
How Docker works
Docker has a client-server design. The docker command you type is the client. It sends requests over an API to the Docker daemon (dockerd), which manages images, containers, networks and volumes. The daemon hands the actual container work to containerd, and containerd uses runc to create the container with the namespaces and cgroups described above.
Images come from a registry. By default it's Docker Hub, but it can be any registry: GitHub Container Registry, Amazon ECR, Google Artifact Registry or your own.
The easiest way to see the whole chain is the hello-world image. Its output literally lists the steps:
shell
1docker run hello-worldshell
1Unable to find image 'hello-world:latest' locally2latest: Pulling from library/hello-world358dee6a49ef1: Pull complete4Digest: sha256:c567b231f65614688711a75f31518a064258a51d442117a3e771a3a8fdba78ef5Status: Downloaded newer image for hello-world:latest6
7Hello from Docker!8This message shows that your installation appears to be working correctly.9
10To generate this message, Docker took the following steps:11 1. The Docker client contacted the Docker daemon.12 2. The Docker daemon pulled the "hello-world" image from the Docker Hub.13 (arm64v8)14 3. The Docker daemon created a new container from that image which runs the15 executable that produces the output you are currently reading.16 4. The Docker daemon streamed that output to the Docker client, which sent it17 to your terminal.18...The same happens with real software. The official Apache HTTP Server image is called httpd (image names are always lowercase):
shell
1docker run -d --name apache -p 8081:80 httpd:2.4shell
1Unable to find image 'httpd:2.4' locally22.4: Pulling from library/httpd3...4Status: Downloaded newer image for httpd:2.455cae7eb21eebc13f79c935c1cbde77d200b560e540830cabf9f957bc528ae769The daemon didn't find the image locally, pulled it from Docker Hub, cached it and started a container. Open localhost:8081 and Apache answers with its "It works!" page. Run the command again with another name and port, and Docker skips the download: the image is already in the local cache.
You don't need a Docker Hub account to pull public images. Anonymous pulls are limited to 100 per 6 hours per IP address, and docker login with a free account raises that to 200. You do need to log in to push your own images.
Docker building blocks
Seven terms cover most of what you'll meet in Docker.
Image
A read-only template with everything an app needs to run: files, libraries, environment variables and the default command. Images are built from layers, and layers are shared between images, so ten images based on the same Alpine base store that base once.
Container
A running (or stopped) instance of an image. Docker adds a thin writable layer on top of the image, and everything the container writes goes there. Remove the container and that layer is gone. You can start many containers from one image.
Registry
A server that stores images and serves them by name and tag, like nginx:1.30-alpine. Docker Hub is the default public registry. Companies usually keep private images in their cloud provider's registry.
Dockerfile
A text file with instructions to build an image: start from a base image, copy files, install packages, set the start command. docker build turns it into an image.
Volume
Persistent storage that Docker manages outside the container's writable layer. Databases keep their data in volumes, so the data survives when the container is removed and recreated.
Network
Containers connect to virtual networks. Containers on the same user-defined network reach each other by name, and you publish ports with -p to make a service reachable from the host. Our guide on how to expose a port in a Docker container covers ports in detail, and connecting to the Docker host from a Docker container covers the opposite direction.
Docker Compose
A tool that describes a multi-container app in one YAML file: services, networks and volumes. One docker compose up starts the whole stack. Compose is built into the Docker CLI as docker compose (with a space).
Your first container in five steps
You need Docker installed. On Linux, install Docker Engine from the official instructions. On macOS and Windows, install Docker Desktop (check the licensing section below first if you're at a company).
Step 1. Check the installation
shell
1docker versionshell
1Client:2 Version: 29.4.23 API version: 1.544...5Server: Docker Desktop 4.72.0 (225998)6 Engine:7 Version: 29.4.28...9 containerd:10 Version: v2.2.311 runc:12 Version: 1.3.5You should see both a Client and a Server section. If the Server part shows an error, the daemon isn't running: start Docker Desktop, or run sudo systemctl start docker on Linux.
Step 2. Run a web server
shell
1docker run -d --name web -p 8080:80 nginx:1.30-alpine-d runs the container in the background, --name gives it a name, and -p 8080:80 maps port 8080 on your machine to port 80 in the container. Check it:
shell
1curl -I http://localhost:8080shell
1HTTP/1.1 200 OK2Server: nginx/1.30.63...You can also open localhost:8080 in a browser and see the NGINX welcome page.
Step 3. List containers and images
shell
1docker psshell
1CONTAINER ID IMAGE COMMAND CREATED STATUS PORTS NAMES2aa7017353c6a nginx:1.30-alpine "/docker-entrypoint.…" 2 seconds ago Up 2 seconds 0.0.0.0:8080->80/tcp, [::]:8080->80/tcp web35cae7eb21eeb httpd:2.4 "httpd-foreground" 6 seconds ago Up 5 seconds 0.0.0.0:8081->80/tcp, [::]:8081->80/tcp apacheshell
1docker images nginxshell
1WARNING: This output is designed for human readability. For machine-readable output, please use --format.2IMAGE ID DISK USAGE CONTENT SIZE EXTRA3nginx:1.30-alpine 0e52bd054126 93.1MB 26.9MB Udocker ps shows running containers (add -a for stopped ones too). docker images lists local images, and U in the EXTRA column means a container uses the image. For the rest of the everyday commands, see our list of Docker commands every Docker expert must know.
Step 4. Build your own image
Create a folder called hello-docker with two files. First, index.html:
html
1<h1>Hello from my first Docker image</h1>Then a Dockerfile next to it:
dockerfile
1FROM nginx:1.30-alpine2COPY index.html /usr/share/nginx/html/index.htmlBuild the image from inside the folder and run it:
shell
1docker build -t hello-docker:1.0 .2docker run -d --name hello -p 8082:80 hello-docker:1.03curl http://localhost:8082shell
1...2#5 [1/2] FROM docker.io/library/nginx:1.30-alpine@sha256:0e52bd05...3#6 [2/2] COPY index.html /usr/share/nginx/html/index.html4#7 naming to docker.io/library/hello-docker:1.0 done5...6<h1>Hello from my first Docker image</h1>That's the whole idea of Docker in two lines of Dockerfile: take a known base, add your app, ship the result as one image. Our guide on how to run a Docker container on your local machine goes deeper into building and running your own app.
Step 5. Run an app and a database with Compose
Real apps rarely live alone. Free port 8080 first by removing the containers from the previous steps:
shell
1docker rm -f apache web helloNow add a compose.yaml to the same hello-docker folder. It runs your web image next to a PostgreSQL database with a named volume:
yaml
1services:2 web:3 build: .4 ports:5 - "8080:80"6 depends_on:7 - db8
9 db:10 image: postgres:18-alpine11 environment:12 POSTGRES_PASSWORD: example13 volumes:14 - db-data:/var/lib/postgresql15
16volumes:17 db-data:Start the stack:
shell
1docker compose up -d2docker compose psshell
1...2 Network hello-docker_default Created3 Volume hello-docker_db-data Created4 Container hello-docker-db-1 Started5 Container hello-docker-web-1 Started6NAME IMAGE COMMAND SERVICE CREATED STATUS PORTS7hello-docker-db-1 postgres:18-alpine "docker-entrypoint.s…" db 5 seconds ago Up 4 seconds 5432/tcp8hello-docker-web-1 hello-docker-web "/docker-entrypoint.…" web 5 seconds ago Up 4 seconds 0.0.0.0:8080->80/tcp, [::]:8080->80/tcpCompose built the web image, pulled Postgres, and created a network and a volume. Both services are on the same network, so web reaches the database simply by its service name:
shell
1docker compose exec web ping -c 1 dbshell
1PING db (172.19.0.2): 56 data bytes264 bytes from 172.19.0.2: seq=0 ttl=64 time=0.105 msThe volume keeps data across container restarts. Write a row, recreate the containers and read it back:
shell
1docker compose exec db psql -U postgres -c "CREATE TABLE notes (body text); INSERT INTO notes VALUES ('still here');"2docker compose down3docker compose up -d4docker compose exec db psql -U postgres -c 'SELECT * FROM notes;'shell
1 body2------------3 still here4(1 row)docker compose down removed both containers and the network, but not the volume, so the data survived.
⚠️ POSTGRES_PASSWORD: example is fine for a local demo only. In real projects keep secrets out of the Compose file, for example in an .env file that isn't committed.
Clean up
shell
1docker compose down -v2docker rmi hello-docker:1.0-v also deletes the volume, together with the data in it.
Docker Engine vs Docker Desktop
These two names cause a lot of confusion, and they have different licenses.
- Docker Engine is the daemon, the CLI and the container runtime. It runs natively on Linux and is open source under the Apache 2.0 license. It's free for any use, including production servers at large companies.
- Docker Desktop is an app for macOS, Windows and Linux. It bundles Docker Engine inside a lightweight Linux VM and adds a GUI, Compose, Buildx, an optional local Kubernetes cluster and other tools.
⚠️ Docker Desktop is free only for personal use, education, non-commercial open-source projects and small businesses with fewer than 250 employees and less than $10 million in annual revenue. Larger companies need a paid Docker subscription (Pro, Team or Business). The details are in Docker Desktop's license terms.
Plenty of teams run Docker Engine directly on Linux workstations and CI runners, and Docker Desktop only on developers' Macs and Windows laptops.
Docker, OCI and the alternatives
Docker is the best-known container tool, but not the only one. The formats are open: the Open Container Initiative (OCI) standardizes the image format, the runtime and the registry API. An image you build with Docker runs with any OCI-compatible tool, and the other way round.
- containerd is the container runtime inside Docker itself. Kubernetes removed its built-in Docker support (dockershim) in version 1.24 and talks to containerd or CRI-O directly. Images built with Docker still run on Kubernetes without changes.
- Podman is a daemonless alternative with a Docker-compatible CLI. It runs rootless when you use it as a regular user, and most
dockercommands work if you just typepodmaninstead. - runc is the low-level tool that actually creates the container. Docker, containerd and Podman can all use it.
If you're moving containers onto Kubernetes, our guide on restarting Kubernetes pods with kubectl is a good next stop.
When Docker fits and when it doesn't
Docker is a great fit when you need:
- The same environment everywhere. Dev, CI and production run the same image, so "works on my machine" stops being an excuse.
- Fast, repeatable CI builds. Every pipeline step runs in a clean container. Read more about it in our post on continuous integration.
- Several services or versions on one host. Postgres 17 and 18, PHP 8.3 and 8.5, side by side without conflicts.
- Third-party software in one command. Databases, queues and monitoring tools for local development.
- A path to Kubernetes. Container images are the unit Kubernetes deploys.
- GPU workloads. With the NVIDIA Container Toolkit, containers get access to the GPU without installing CUDA on every host. See our guide on running NVIDIA CUDA inside a Docker container.
Think twice when:
- You need hard isolation between untrusted tenants. A shared kernel is a shared attack surface. Use VMs or a sandboxed runtime.
- The app needs a different kernel or OS. Linux containers can't run a Windows app or a custom kernel module that the host doesn't have.
- You run stateful databases in production without a plan. Containers make it easy to start a database, not to back it up, upgrade it and restore it. Managed databases are often the better call.
- You need to run many containers across many servers. Docker alone won't schedule, heal or scale them. That's a job for an orchestrator like Kubernetes.
Wrapping up
Docker is a client, a daemon and an image format that make Linux containers easy to build, share and run. Containers share the host kernel, so they're lighter than VMs but less isolated. And they usually run on VMs anyway, especially in the cloud.
From here, try the five steps above with your own app, then dig into Docker commands, ports and running containers locally. For a production example, see how we ran an online dating app in Docker for high availability.
If you're moving production apps into containers or onto Kubernetes, our Kubernetes consulting and DevOps automation and CI/CD teams do this every day. Get in touch and tell us what you're running.